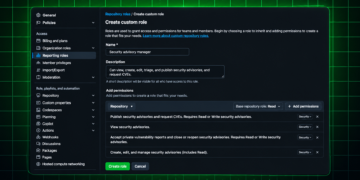
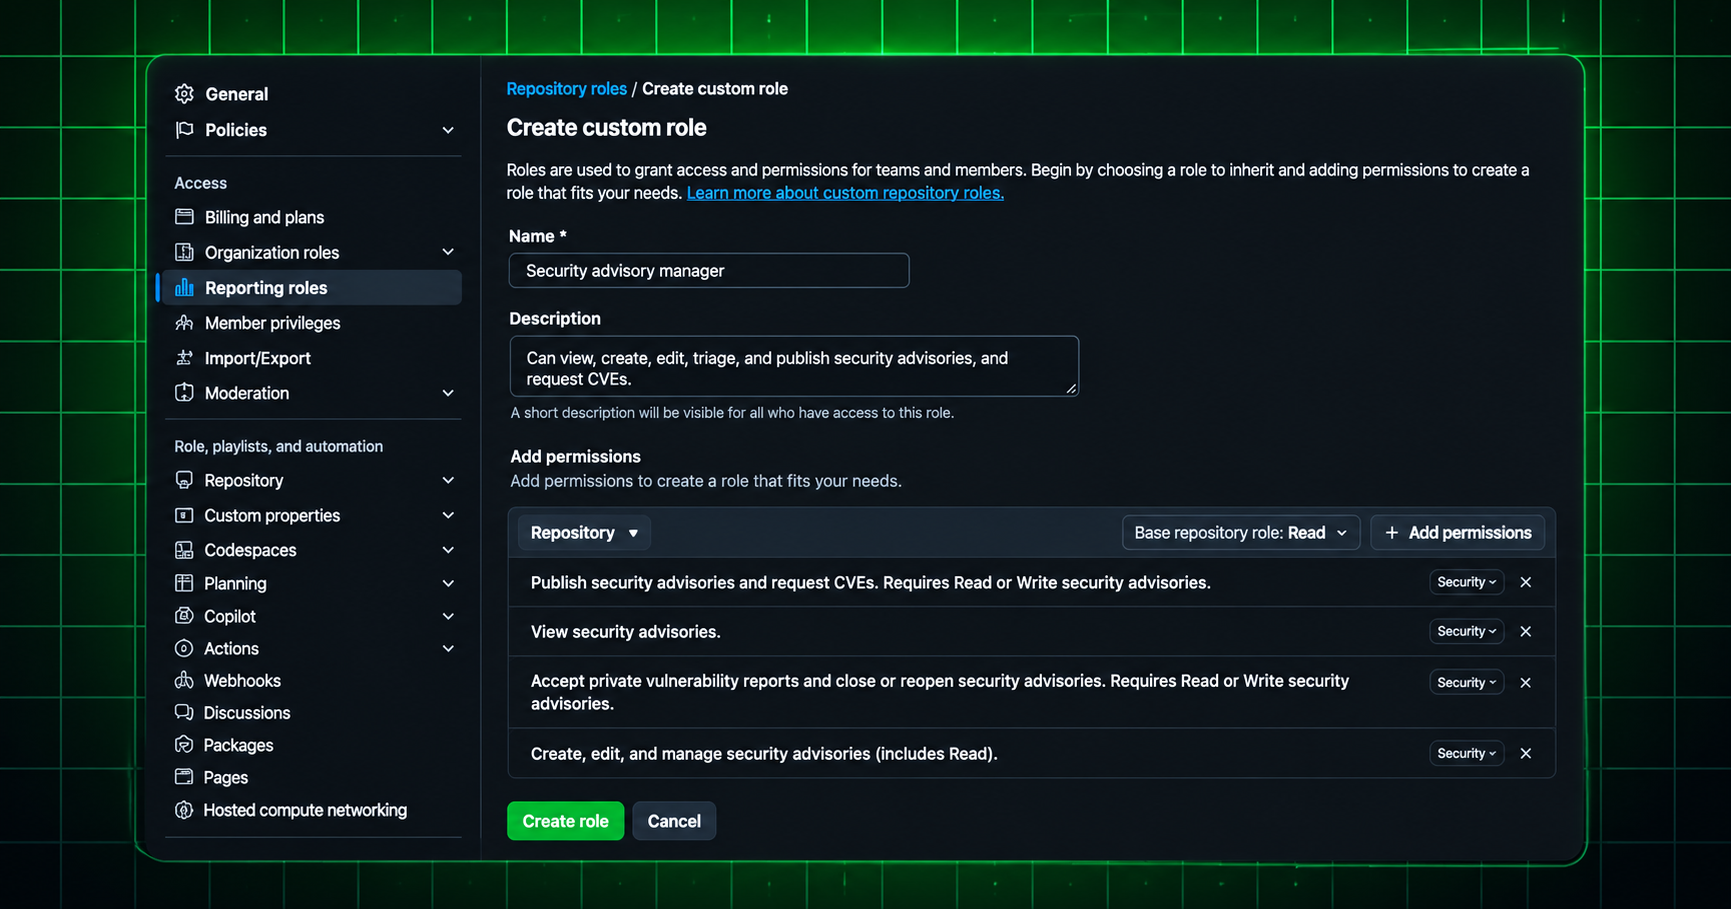
GitHub has made dedicated security advisory permissions generally available, allowing organisations to assign people responsibility for repository security advisories and private vulnerability reports without giving them all repository administrator privileges.
Security work can be assigned more narrowly
The November 20 release allows organisation owners to configure custom repository roles for teams handling vulnerabilities. Those permissions apply to repository security advisories and private vulnerability reporting. They do not grant unrestricted visibility into advisories for every repository in the organisation.
Availability is not universal
GitHub says the feature is available on plans supporting custom repository roles, including GitHub Enterprise Cloud. Organisations using other plans cannot assume the feature is available simply because the update is generally available. Administrators should confirm their plan and role settings before revising internal processes.
Access controls still require governance
Separating security permissions from broad administrative authority can reduce unnecessary access. The change does not independently prove an improvement in vulnerability response time, nor does it mean disclosure reports will be reviewed without assigned personnel. Organisations still need workflows for triage, fixes and coordinated disclosure. GitHub has not published measured time savings for the release.